Showing posts with label adsiedit. Show all posts

Wednesday, October 28, 2009

The properties on have invalid data. If you click OK, default values will be used..

A customer had a user with a mailbox throwing the following error whenever they tried to change a value:

The properties on [recipient] have invalid data. If you click OK, default values will be used instead and will be saved if you do not change them before hitting Apply or OK on the property page. If you click cancel, the object will be displayed read-only and corrupted values will be retained.

OK no problem, I'll just go in and get rid of anything that doesn't look right...wrong. The console wouldn't let me save the settings.
Apparently the storage quotas were such that the Prohibit Send Limit value was less than the Warning Limit. I was, however, unable to modify it in ADUC/DSA or in the EMC.

I attempted to change the value in EMS, but it threw the exact same error.

When finesse isn't enough, brute force wins. I popped open adsiedit.msc by launching adsiedit.msc from 'Run,' then navigated to where the user resided under Domain -> User OU, right clicked, and clicked properties. Sure enough the EMC and EMS were lying to me:


I modified the values to what I wanted them to be:
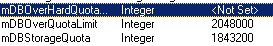


Voila.. Invalid Data errors are gone.

Thursday, September 25, 2008

Using LDIFDE & ADSIEdit to Verify Recipient Policies

Originally I wanted to run something like this:

ldifde -f C:\test.txt -t 3268 -s DC.domain.com -j C:\ -r "(&(|(mailnickname=*)(objectClass=user))(|(homeMDB=*)(msExchHomeServerName=*))(userPrincipalName=*@domain.com))" -l "msExchPoliciesIncluded"

Unfortunately userprinicipalname doesn't play nicely with  "msExchPoliciesIncluded."  I'm guessing this is the case with more than one user defined attribute.  Example output:

dn: CN=sname\, gname,OU=Users-Company,OU=User,DC=Corp,DC=com
changetype: add


If we change it to reflect only objectclass=user:

ldifde -f C:\test.txt -s DC.domain.com -j c:\ -r "(&(objectClass=user)(homeMDB=*))" -l "msExchPoliciesIncluded"

It pulls this as example:

dn: CN=sname\, gname,OU=User,DC=domain,DC=Corp,DC=com
changetype: add
msExchPoliciesIncluded
 {86129EE7-F6C7-4CE2-9549-C242356184C6},{3B6813EC-CE89-42BA-6F11-D87D4AA30DBC}
msExchPoliciesIncluded
 {7DF5DEB4-C2EA-4920-BC8C-5342BC1E95E6},{26491CFC-4EB1-4857-861B-0CB8DF22B5D7}

You can also find this in adsiedit here to verify: